Orbis Sign

Evidence and records

Electronic signature audit trails: what to record and how to read them

An audit trail is useful when each event has a clear source, meaning and relationship to the document. More rows do not automatically mean stronger evidence.

What an audit trail is

In electronic signing, an audit trail is a chronological record of selected workflow events. It may cover creation, sending, consent, field completion, signature submission, reminders and overall completion. It is normally supporting evidence beside the executed document, not a magical certificate that settles every possible dispute.

First identify provenance. Some events are produced by the signing application; others may be callbacks from an email or SMS provider; some browser or network values may be reported by a client. Labels such as “opened” or “delivered” need definitions. Provider delivery can mean acceptance by downstream infrastructure, while an open signal may be generated by privacy software and does not prove careful reading.

Questions to ask of every event

  • Source: Which application, server, provider or browser supplied it?
  • Subject: Is it linked to a document, recipient, invitation, field or completed file?
  • Time: Which clock and time zone produced the timestamp?
  • Meaning: What exact condition creates the event, and can it occur more than once?
  • Integrity: Can later changes be detected, and what bytes or record does any hash cover?
  • Limits: What does the event not establish—for example, identity, authority or comprehension?

Reading Orbis Sign records carefully

Orbis Sign can expose selected workflow, consent, signing and provider-reported events. Coverage varies and should not be described as every interaction. Recorded browser or network information does not independently prove who used the device. Document states and reminders help teams manage work but are not legal conclusions.

At completion, the application records a SHA-256 value over the completed PDF bytes and checks it again when the PDF is served. If the completed PDF cannot be produced, the document is not marked complete. Even so, never state that a value verifies the final document unless it was actually calculated over that document’s bytes and the verification process is defined.

Retention and access

Decide who owns the completed PDF and supporting record, where they are filed, who may retrieve them and how legal holds work. Retention should reflect purpose, limitation periods, regulatory duties and data minimisation. A platform’s availability is not a customer retention policy, and indefinite storage should not be assumed.

Audit records contain personal data and potentially sensitive transaction context. Apply role-based access, review exports and deletion, and evaluate supplier and hosting arrangements. The ICO provides official UK GDPR security guidance; it does not prescribe one universal electronic-signature record.

A review checklist

  1. Download the completed file and its separate supporting record.
  2. Check document title, parties, recipients and completion status.
  3. Distinguish application events from provider-reported signals.
  4. Verify what any checksum covers before relying on it.
  5. Record exceptions, corrections or manual verification undertaken.
  6. File evidence under an approved retention and access policy.

For the wider workflow context, see how electronic signatures work and the Orbis Sign security overview.

This is general practical information, not legal advice. Electronic execution is not suitable for every document. Check the law, agreed formalities and your organisation’s requirements for the transaction.
Review the evidence your workflow needs

Start a 7-day free trial with no card, or tell us what you need to send, who needs to act and how you need to retain the result.

Audit trail and certificate of completion: two views of one record

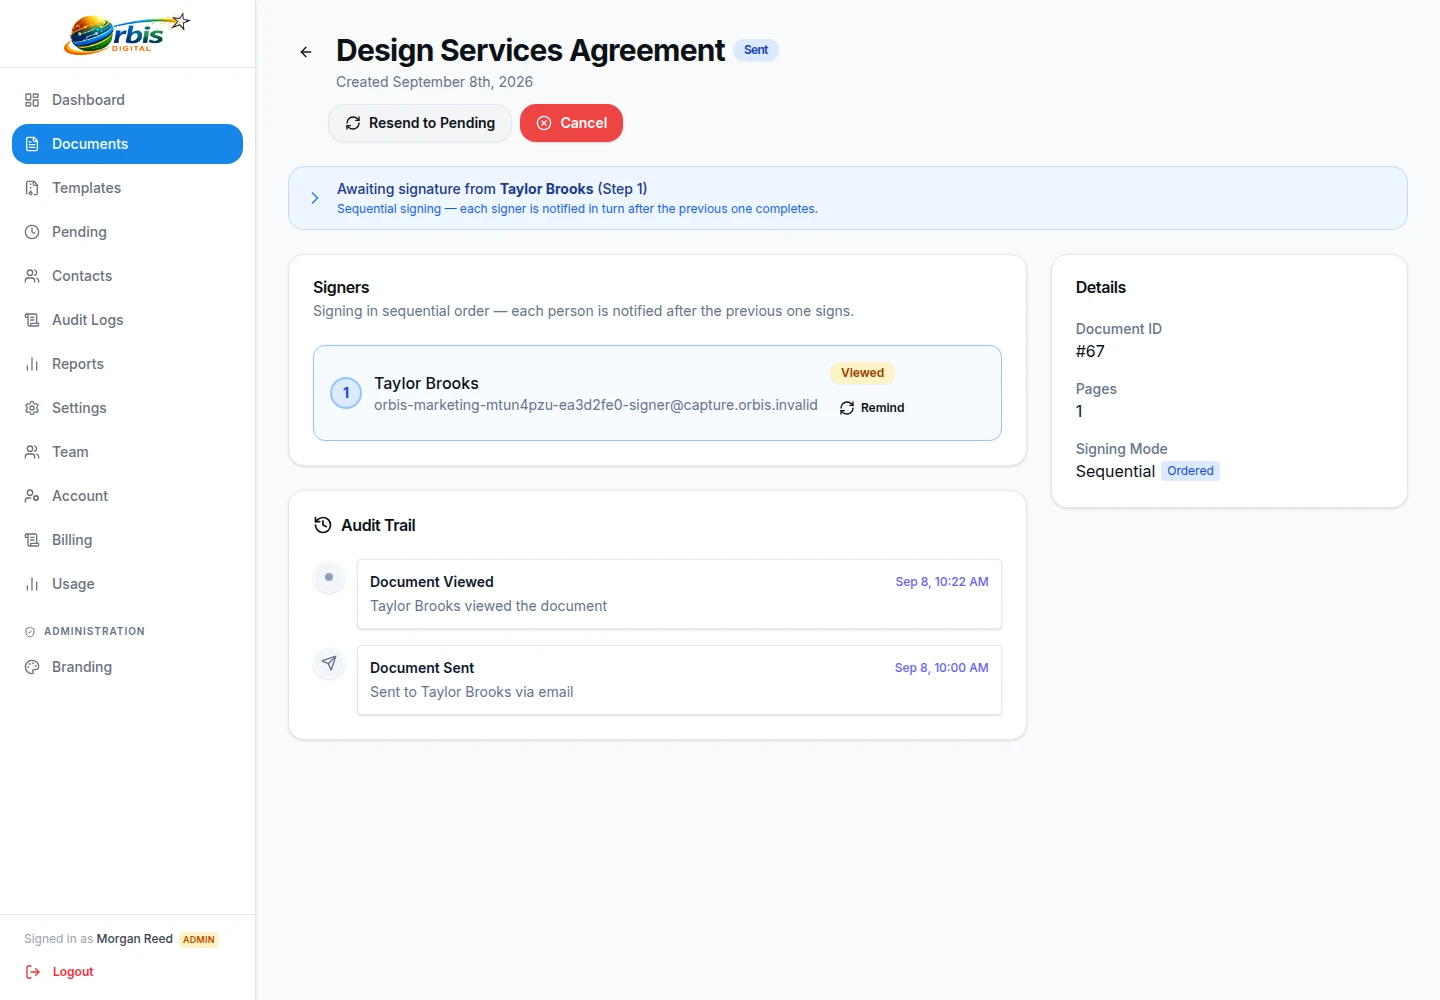
In Orbis Sign the audit trail appears in two places. Inside the app, each document has an audit page showing its status, each signer’s progress and a list of events with times. That is the working view, used while a document is out for signature and afterwards when someone asks what happened.

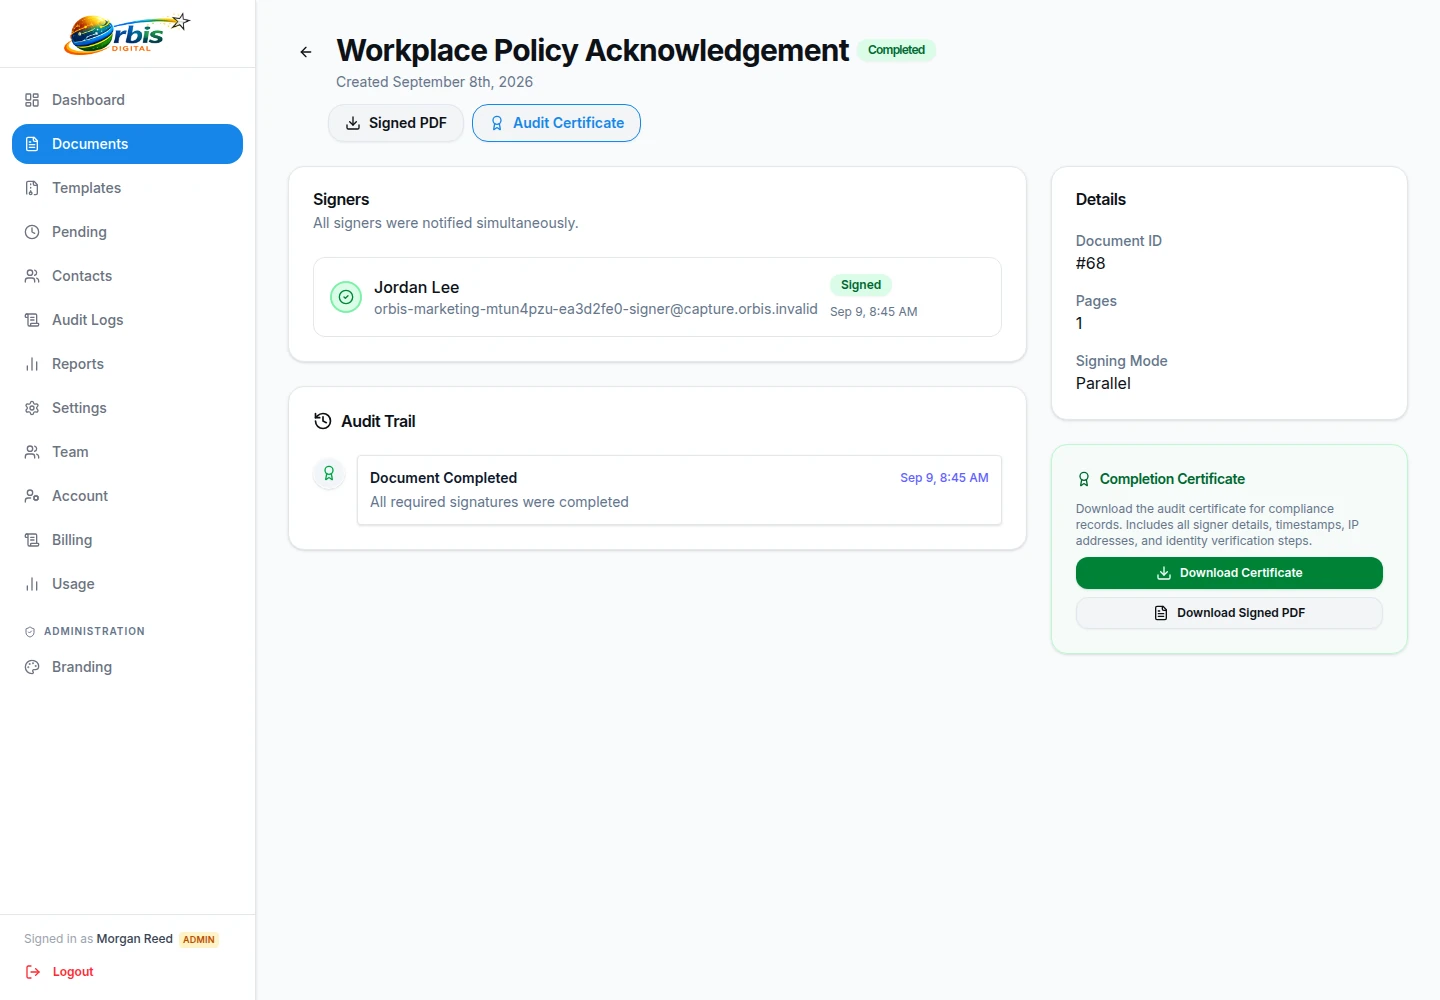
When the document completes, the same information is summarised in a separate certificate, sometimes called an e-signature certificate of completion. It sits beside the signed PDF rather than inside it, so the agreement itself stays clean and the evidence can be read on its own. Both the PDF and the certificate are sent to every signer and can be downloaded by authorised users. You can follow a live document on the document tracking page.

Orbis Sign sent document screen showing recipient status and the audit trail

What the Orbis Sign certificate contains

The certificate is deliberately limited to facts the service records directly. It contains the following.

For each signer

Their name and email address, their phone number where SMS was used, their status, the time they signed and the IP address recorded when they signed. If the document used a one-time passcode, the certificate shows that their email address was verified. It also records the version of the consent-to-sign-electronically wording they accepted.

Events and times

A table of events for the document, such as sending, opening, viewing and signing, each with its time. This lets a reader follow the order in which things happened.

The document hash

The SHA-256 hash of the completed PDF, calculated when field values and signatures were written into it. This connects the certificate to one specific file.

Orbis Sign completed document screen showing download actions and the audit trail

Who receives the certificate, and how to get it later

When a document completes, every signer receives the signed PDF and the certificate by email. If your workspace has a support email set in its branding, a copy goes there too, which is a simple way to make sure the business always has its own set. The certificate carries your company name, logo and colours alongside a “Powered by Orbis Sign” line.

Later, anyone in your workspace with permission to see the document can download both files from the document page. Downloads are per document; there is no bulk export of certificates. Orbis Sign does not delete completed documents automatically, but you can delete one permanently, after which the files are gone. Keep your own copies in whatever system you use for business records.

Hands holding a phone over a desk

Checking a signed PDF against its recorded hash

Because the certificate shows the SHA-256 hash of the completed PDF, you can check a copy yourself. Calculate the SHA-256 hash of the file you hold using a standard tool, such as the built-in hashing commands on Windows, macOS or Linux, and compare it character by character with the value on the certificate.

If the two match, the file is the same, byte for byte, as the one recorded at completion. If they differ, the file has been changed in some way, even if it looks identical; re-saving a PDF in another program can be enough. Orbis Sign runs the same comparison whenever the PDF is downloaded from the app. A matching hash is good evidence about the file. It says nothing about who signed it or whether they were entitled to.

Hands typing on a laptop seen from above

What an audit trail cannot prove

A certificate is a record of what the service observed, and that has limits. It shows that someone using a particular link, and where used a passcode sent to a particular inbox, completed the signing steps at a recorded time. It does not prove that the named person was the one at the keyboard, that they had authority to sign for a business, or that they understood the document.

An IP address identifies a network connection at a moment, not a person or a precise location. A verified email shows access to that inbox, not exclusive access. These records support your own record-keeping; they do not independently establish identity, authority or legal effect. Where those matter, add checks outside the signing process. This is general information, not legal advice.

Two colleagues reviewing papers at a table

Reading document and signer statuses

Statuses give a quick view of where things stand. A document moves from Draft to Pending once sent, then to Partly signed when some but not all signers have finished, and to Completed when the last one signs. It can also end as Cancelled or declined, or Expired if the deadline passes.

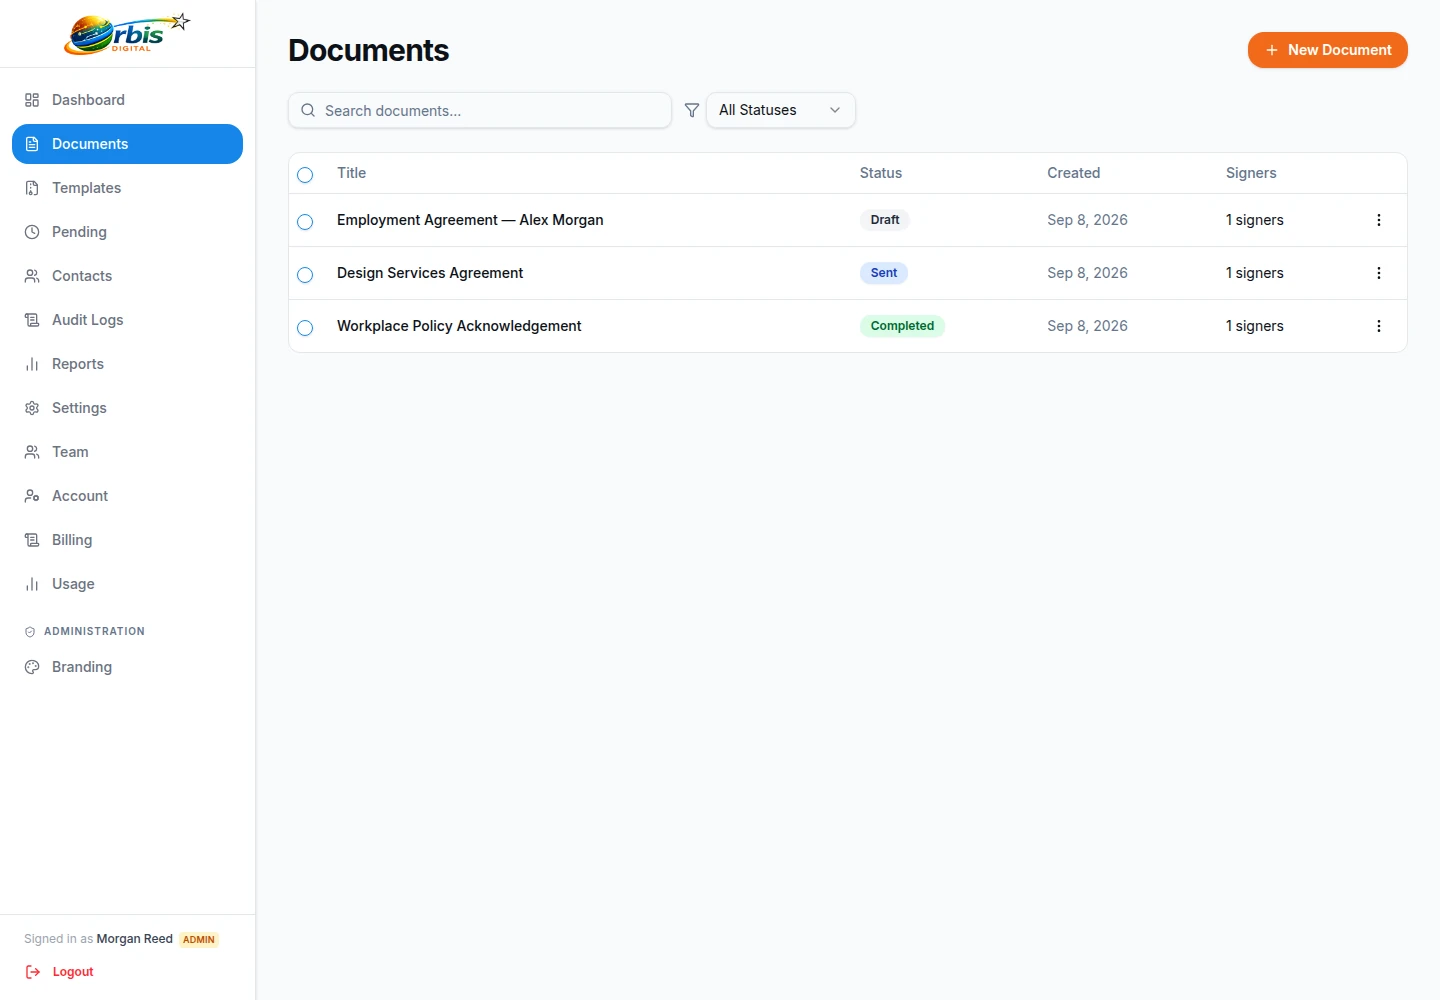
Each signer has their own status too: sent, opened, viewed, signed or declined. Treat “opened” and “viewed” as signs that the link or document was accessed, not as proof that anyone read it carefully. The documents list can be searched by title and filtered by status, and the reports show a status breakdown, documents per month and average time to sign, with CSV export.

Orbis Sign document list screen showing search and a status filter

Retaining audit records responsibly

Certificates contain personal data: names, email addresses, IP addresses and sometimes phone numbers. Handle them like any other record that identifies people. Decide how long you need to keep signed agreements and their certificates, and who in the business should be able to see them. Orbis Sign’s roles and custom permissions help limit who can open documents inside the app.

Orbis Sign runs on servers in France, in the EEA, operated by Orbis Digital Ltd of Newcastle upon Tyne. The team security audit log records changes to who has access. More detail is on the security page.

A team gathered around a desk with open folders

If a signature is questioned

Suppose, hypothetically, that a lettings agency is told by a tenant that they never signed a renewal form. The agency would start by downloading the signed PDF and certificate, checking the PDF’s hash against the certificate, and noting the signer’s email address, signing time and whether a passcode was used.

It would then gather the evidence that sits outside Orbis Sign: correspondence before and after signing, how the email address was obtained, any payment or behaviour consistent with the agreement. The certificate is one part of that picture. For anything likely to become a formal dispute, the agency would take legal advice rather than rely on the record alone.

A manager pointing at a paper while two seated colleagues read it

Audit trails and certificates: common questions

What is an e-signature certificate of completion?

It is a separate document produced when an electronically signed document is completed. In Orbis Sign it lists each signer’s name, email, status, signing time and IP address, the consent version they accepted, an event table with times and the SHA-256 hash of the completed PDF. It supports your own records but does not prove identity or authority on its own.

Does the certificate show where the signer was?

No. It records the IP address seen when the signer signed. An IP address identifies a network connection at a point in time and is not a reliable guide to a person’s exact location. The certificate does not include GPS or other location data.

Can I download certificates for all my documents at once?

No. Downloads are per document: from each document page you can download the signed PDF and its certificate. Every signer, and your support email if set, also receives both by email when the document completes, so many businesses file them as they arrive.

Is the certificate itself digitally signed?

No. Orbis Sign does not apply certificate-based digital signatures or seals to the signed PDF or the certificate. The certificate records the SHA-256 hash of the completed PDF, which you can use to check whether a copy has changed since completion.

Do signers get a copy of the audit certificate?

Yes. When the last person signs, every signer receives the completed PDF and the certificate by email. Your workspace support email receives a copy too if one is set in your branding settings, and authorised users can download both from the app.

Does the audit trail show whether someone read the document?

Not reliably. Statuses such as opened and viewed show that a link or document was accessed. They do not show how long someone spent reading or whether they understood it. The signing record shows that the signer ticked consent and completed their fields.