Orbis Sign

Security & data protection

Layered controls for signing workflows

Orbis Sign uses layered controls designed to protect accounts, documents and signing workflows.

Last updated: 27 October 2026

Account and workspace access

Database-user passwords are stored as salted scrypt hashes rather than plaintext. Authenticated sessions are held server-side and identified by an HttpOnly, SameSite=Lax cookie with an eight-hour maximum age and the Secure attribute in production. Optional authenticator-app two-factor authentication is implemented.

Server routes derive the current workspace from an active membership and apply role checks. Separate permissions protect privileged platform functions.

Signing links and evidence

Recipient links use random tokens with an expiry. A Customer can require a one-time passcode for a workflow. Assigned-field checks limit a Signer to fields intended for that Signer or shared fields. The service records express electronic-signing consent and selected status, signing and workflow events.

When a document is completed, Orbis Sign records a SHA-256 hash of the completed PDF and checks it again whenever that PDF is served. If the completed PDF cannot be produced, the document is not marked complete. A downloadable HTML audit certificate presents available workflow evidence separately from the completed PDF.

Audit data can include timestamps, server-observed or reported network and browser information, recipient details and delivery events where captured. It supports an evidence review but does not conclusively prove civil identity, authority, capacity, location, legal validity or an unbroken chain of custody.

Application safeguards

  • Same-origin Origin or Referer checks for state-changing requests authenticated by session cookie.
  • Origin allow-listing, API security headers and production rate limits for sensitive routes.
  • Server-side input validation on key account, document and signing workflows.
  • Redaction of authorisation and cookie headers from application request logs.
  • Provider-signature verification where Stripe webhooks are used, and fail-closed shared-secret checking for configured Brevo webhooks.

Data handling and infrastructure

Original PDFs are held in PostgreSQL and completed PDFs in private file storage on the same servers. Access is mediated by authenticated application workflows and workspace permissions. Production sessions use secure cookie settings and the API enables HSTS in production configuration.

Orbis Sign is hosted by Orbis Digital Ltd on dedicated servers in the EU (France). It does not promise UK-only data residency, a particular recovery region, a fixed backup frequency or recovery objective. Customer-specific commitments apply only where they are included in an Agreement.

Important limitations

Security controls reduce risk but no online service can guarantee absolute security. This page is not a certification, independent audit opinion, penetration-test report, service-level agreement or legal warranty. Orbis Sign does not claim ISO 27001, SOC 2, Cyber Essentials or PCI DSS certification.

Permanent individual-document deletion removes operational document records and unreferenced PDF data from the application database while retaining limited metadata-only security evidence. It is not a tenant-erasure or backup-deletion process. A workspace request or in-product status is not confirmation of complete erasure. See the Privacy Policy and Data Processing Agreement.

Report a security concern

Use the contact form and select technical support, or email . Describe the affected feature and impact without including signing tokens, passwords, one-time codes, private documents or unnecessary personal data. No public response-time SLA is promised.
Read legal and trust information

Secure electronic signatures: what Orbis Sign actually does

Security pages are often long on reassurance and short on detail. This one sets out the specific controls Orbis Sign uses to protect signing requests, completed documents and your workspace, and is clear about where those controls stop.

In short, each signer gets a unique, random link that expires; you can add an email passcode; consent to sign electronically is recorded; the completed PDF is fingerprinted with a SHA-256 hash that is checked when it is downloaded; an audit certificate records what happened; and workspace access is governed by roles, permissions and two-factor authentication. The how it works page shows where each of these fits in the process.

A laptop showing a padlock on screen

Unique signing links with a fixed expiry

Each signer receives their own link containing a long random token, so links cannot be guessed and are not shared between people. Links and the document share one deadline, seven days by default and adjustable from one to 365 days. After it passes, the document expires and the links no longer work.

If you cancel a document, or a signer declines it, all its links stop at once. Because anyone holding a link could open it, signers should not forward their invitation, and senders should check email addresses and mobile numbers carefully before sending.

A hand holding a phone outdoors

An optional one-time passcode by email

For documents that need an extra check, you can require an email one-time passcode. Before opening the document, the signer is sent a code that is valid for ten minutes and must enter it. The audit certificate then shows that the signer’s email was verified.

It is worth being precise about what this shows. A passcode confirms that the person signing could access that email inbox at the time. It does not confirm their identity in any wider sense. For many everyday documents that is a reasonable extra step; for higher-risk transactions you may want further checks of your own.

A woman reading her phone beside a window

Consent to sign electronically, recorded

Before signing, every signer must tick to confirm they agree to sign electronically. Orbis Sign records that consent along with the version of the disclosure they were shown, so you can later see exactly which wording applied.

Signers can also decline, with an optional reason, rather than being pushed to sign. Declining cancels the document and stops every link. Together these give you a clearer record that each signer chose to sign electronically and was not simply clicking through.

A woman typing on a tablet keyboard at a round table

A SHA-256 hash to show the PDF has not changed

When a document is completed, Orbis Sign writes the signatures and field values into the PDF and calculates a SHA-256 hash of the result. A hash is a short fingerprint of the file: change even a single character and the fingerprint is completely different.

The hash is recorded and checked again each time the completed PDF is downloaded from the app, and it is printed on the audit certificate. If anyone later questions whether a copy has been altered, the hash of that copy can be compared with the one on the certificate. Our audit trail guide explains this in more depth.

Hands typing on a laptop seen from above

The audit certificate and its limits

Each completed document comes with a separate audit certificate. It lists each signer’s name, email, phone number where used, status, signed time and IP address, whether their email was verified by passcode, the consent disclosure version, a table of events with times, and the document hash. Every signer receives it by email with the signed PDF.

The certificate is a strong aid to record-keeping. It does not independently prove a signer’s identity, their authority to sign for a business, or the legal effect of the document. Orbis Sign provides simple electronic signatures, not advanced or qualified ones, and this is general information rather than legal advice.

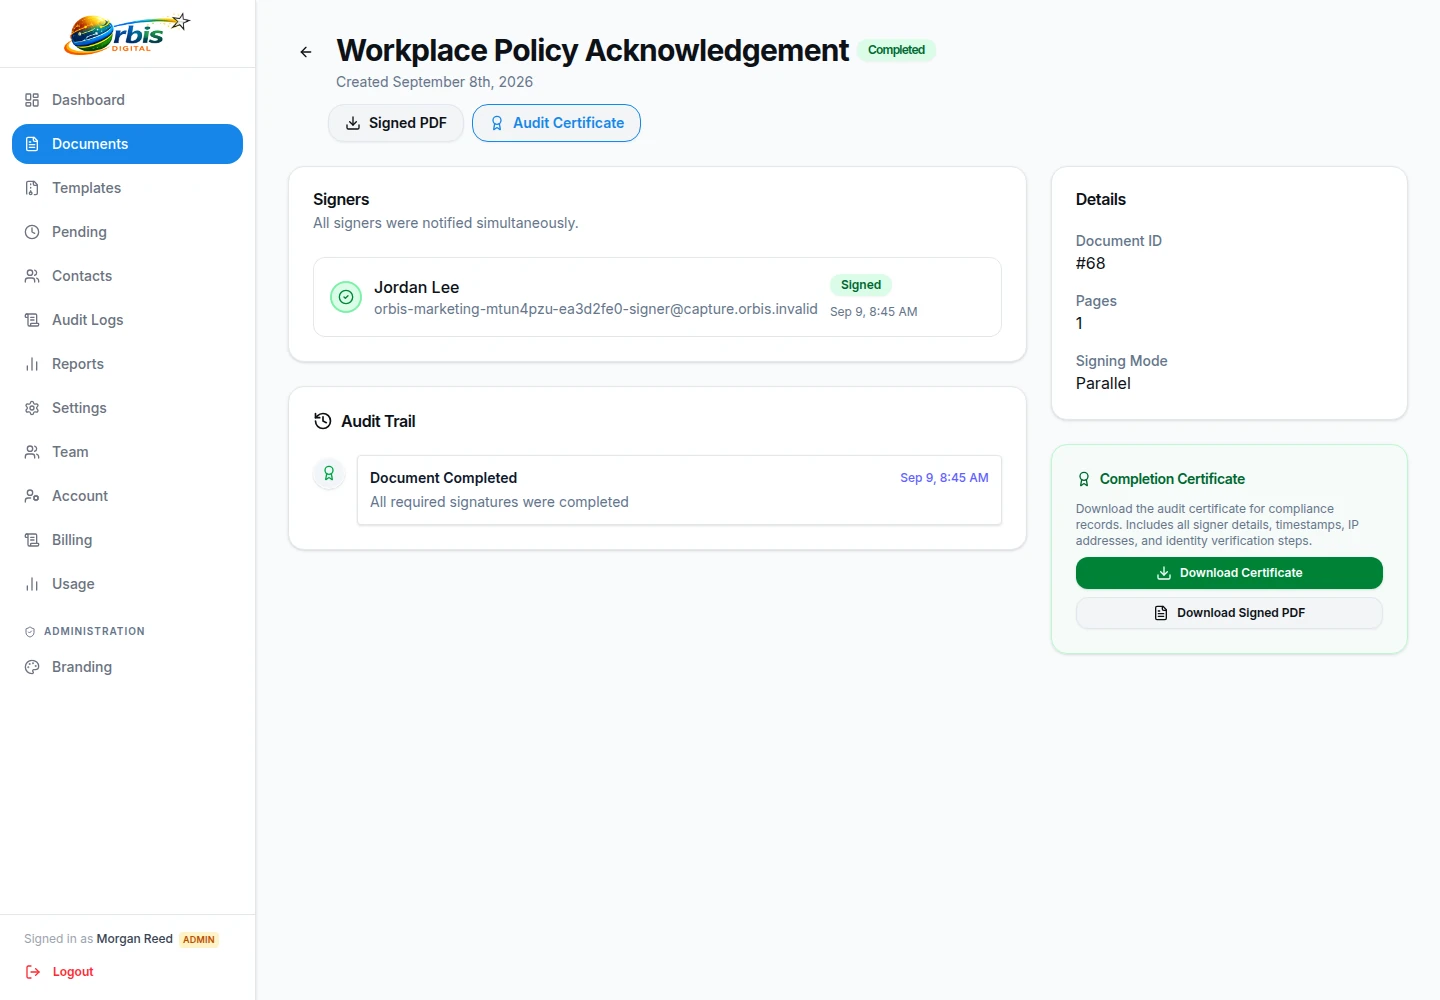
Orbis Sign completed document screen showing download actions and the audit trail

Roles and permissions inside your workspace

Not everyone in a business needs to do everything. Orbis Sign has three standard roles, Owner, Admin and User, and you can build custom roles from detailed permissions, for example letting someone send documents but not manage templates or see reports.

Colleagues join by email invitation, which you can resend or revoke if it was sent to the wrong person or is no longer needed. Billing is controlled by the owner. The team management page has more on setting this up.

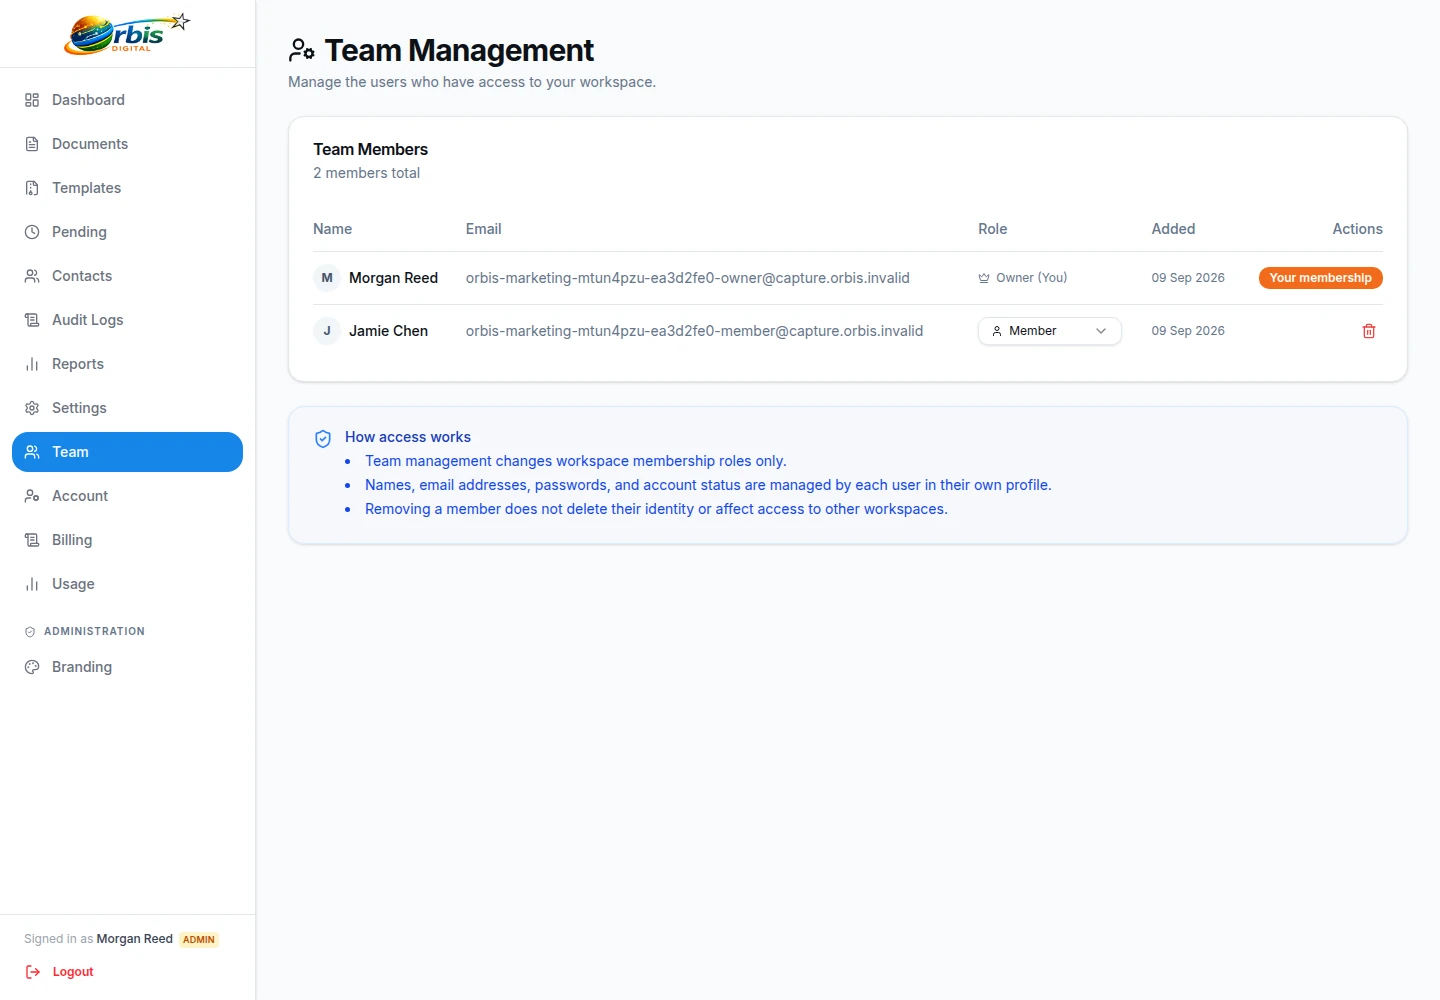
Orbis Sign team screen showing team members and their roles

Two-factor authentication and the team security audit

Users can protect their sign-in with two-factor authentication using an authenticator app, with backup codes for when the phone is not to hand. A workspace policy can require two-factor authentication for chosen roles, so you can insist on it for owners and admins while leaving it optional for others, or require it for everyone.

The team security audit log records security-related activity in the workspace, which helps you review who has changed what and spot anything unexpected.

Hands holding a phone over a desk

Data location, retention and permanent deletion

Orbis Sign runs on servers in France, within the European Economic Area, operated by Orbis Digital Ltd. Documents are not deleted automatically, so you decide how long to keep them in line with your own retention policy.

When you no longer need a document, you can delete it permanently. Do this only after you have downloaded the signed PDF and audit certificate if you need to keep them, because there is no undo and no bulk export. More about the company behind the service is on the about page.

A laptop on an office desk in front of shelves of folders

E-signature security: common questions

Is my data stored in the UK?

No. Orbis Sign runs on servers in France, within the European Economic Area, operated by Orbis Digital Ltd. If your organisation has rules about where data may be held, check them before you start.

Does Orbis Sign hold ISO 27001, SOC 2 or Cyber Essentials certification?

No. Orbis Sign does not claim those certifications. This page describes the controls the product actually uses, such as expiring signing links, optional passcodes, recorded consent, a SHA-256 completion hash, roles and two-factor authentication.

What happens if a signer forwards their link?

Whoever holds the link could open the document, which is why signers are asked not to forward it. For sensitive documents, turn on the email one-time passcode, so a code sent to the signer’s own inbox is needed before the document opens.

Does the audit certificate prove who signed?

Not on its own. It records names, email addresses, times, IP addresses, consent and any passcode verification, which supports your records. It does not independently prove a person’s identity or their authority to sign.

Can I make two-factor authentication compulsory?

Yes. A workspace policy can require two-factor authentication for the roles you choose, such as owners and admins, or for everyone. Users set it up with an authenticator app and keep backup codes in case they lose their phone.